
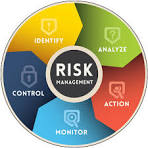
Risk Identification and Vulnerability Assessment: The First Line of Security Defence
Security incidents rarely occur in isolation. In many cases, they exploit weaknesses that already exist within an organisation. Risk identification and vulnerability assessment therefore play a critical role in helping organisations understand what can go wrong, where they are exposed and what should be done before an incident occurs.
What the Data Tells Us
Evidence from the World Bank’s Nigeria Enterprise Survey shows the financial importance of identifying security risks early. The survey found that 20% of formal-sector firms experienced losses from theft, robbery, vandalism or arson, while about 70% paid for security services. The average security expenditure was approximately 1.8% of annual sales. (World Bank)
More recent World Bank business survey evidence also found that 6% of firms reported losses from theft, robbery, vandalism, arson or internet-related fraud in the previous 30 days, with the rate rising to about 15% among large firms. (World Bank)
These figures demonstrate an important lesson: security risk is not only a security department issue. It can directly affect business continuity, finances and organisational performance.
Case Study: The Unprotected Warehouse
Consider a hypothetical logistics company that repeatedly experiences stock shortages. Management initially assumes that the problem is poor inventory control. A vulnerability assessment, however, identifies several weaknesses:
- Poor access control to the warehouse.
- Inadequate CCTV coverage.
- Visitors entering without proper verification.
- Weak inventory reconciliation.
- Poor lighting around the perimeter.
- Inadequate monitoring of loading and dispatch activities.
The problem is therefore not simply “missing stock”. The assessment reveals a combination of physical, procedural and human vulnerabilities that create opportunities for theft.
Instead of responding only after losses occur, management can introduce layered controls, including improved access control, CCTV coverage, inventory reconciliation, visitor management and stronger supervision.
The Risk Identification Process
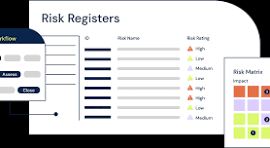
An effective vulnerability assessment should examine:
- Assets: What needs protection?
2. Threats: What could cause harm or loss?
3. Vulnerabilities: What weaknesses could be exploited?
4. Impact: What would happen if the risk materialized?
5. Likelihood: How probable is the event?
6. Controls: What measures are already in place?
7. Gaps: Where are existing controls inadequate?
8. Mitigation: What additional measures are required?
The Key Lesson
You cannot effectively manage a risk that you have failed to identify. Organisations should conduct regular security surveys, vulnerability assessments and risk reviews rather than waiting for an incident to expose weaknesses.
Risk identification should ultimately move an organisation from “What happened?” to “What could happen, and what can we do about it now?”
For organisations operating in Nigeria’s complex security environment, developing this capability is essential for protecting people, property, information, operations and reputation.